
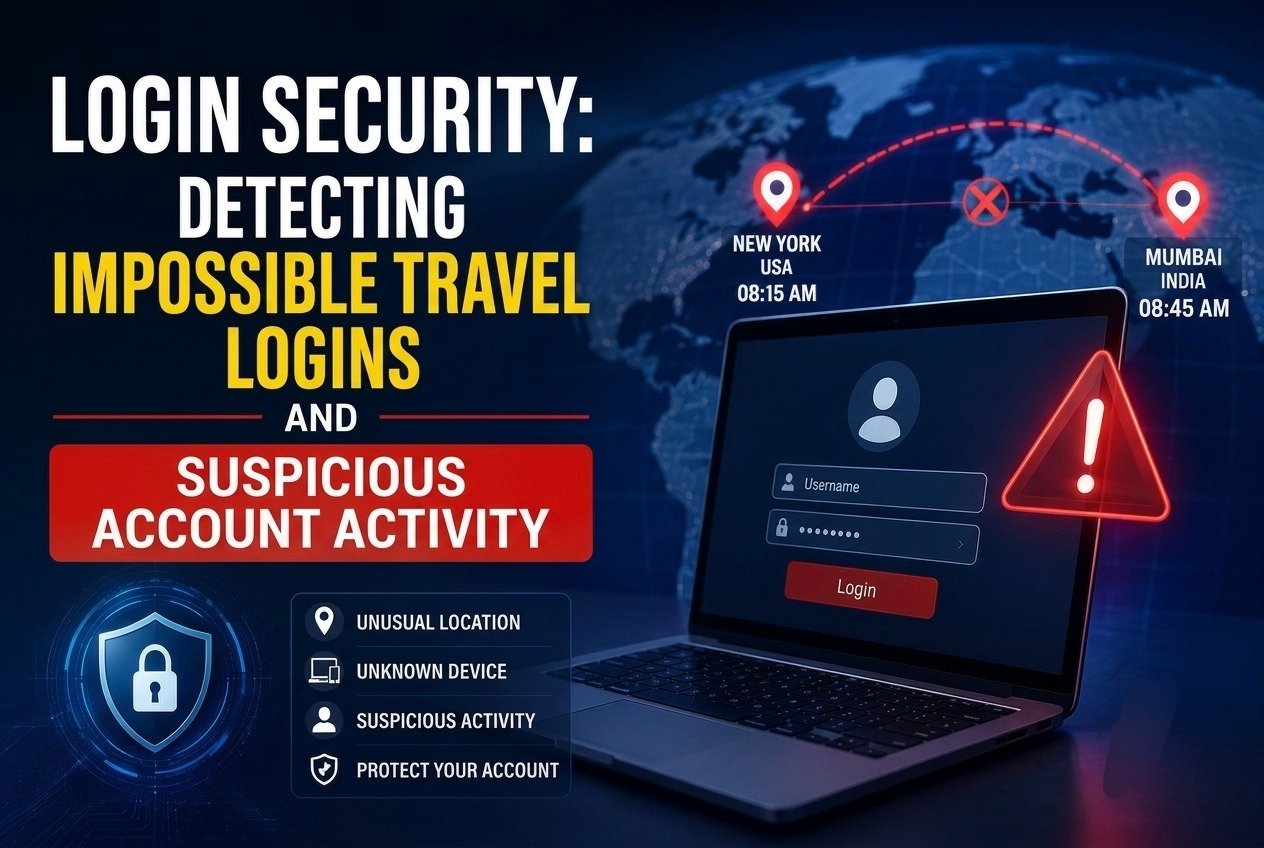
Login Security: Detecting Impossible Travel Logins and Suspicious Account Activity
Login security is an important part of protecting user accounts and web applications from unauthorized access. Cybercriminals often use stolen credentials to access accounts from unusual locations or devices. Detecting suspicious login behavior can help organizations identify potential account compromise before serious damage occurs.
What Are Impossible Travel Logins?
An impossible travel login occurs when the same user account appears to log in from two geographically distant locations within an unrealistic period of time. For example, if a user logs in from India and then appears to access the same account from another country within a few minutes, the activity may indicate that the account credentials have been compromised.
Identifying such login patterns can strengthen account protection and support a broader Web Application Security strategy. Learn more about securing web applications:
https://www.rashicore.com/web-application-security.php
How Login Security Helps Prevent Account Compromise
Strong login security combines monitoring with protective controls such as multi-factor authentication, device recognition, session management, and unusual behavior detection.
When suspicious activity is detected, organizations can require additional identity verification, temporarily restrict access, or alert security teams. These measures help reduce the risk of stolen credentials being used to gain unauthorized access.
For stronger protection against login-based threats and web attacks, explore:
https://www.rashicore.com/web-application-security.php
Best Practices for Secure Login Protection
Businesses should regularly monitor authentication logs, enforce strong password policies, enable multi-factor authentication, and review unusual login behavior. It is also important to secure user sessions and quickly investigate account activity that does not match normal user behavior.
Conclusion
Impossible travel detection is an effective way to identify suspicious account access and potential credential compromise. By monitoring login locations, devices, and user behavior, organizations can detect threats earlier and reduce the risk of unauthorized access.
A strong login security strategy is an important part of protecting modern websites and digital applications. Learn more about comprehensive Web Application Security solutions:
 UK
 USA
 UAE
 Canada
 Australia
 Germany
 Singapore
 Netherlands